We've Open Sourced the Bomfather Agent 🥳
Aug 28, 2026
The Bomfather Agent is now open source. It is an eBPF-based runtime security agent that uses Linux Security Module hooks to enforce simple, executable-based policies directly in the kernel.
The Bomfather Agent is now open source. It is an eBPF-based runtime security agent that uses Linux Security Module hooks to enforce simple, executable-based policies directly in the kernel.
Modern machine learning workloads are somewhat paradoxical, GPUs are more powerful than ever, yet the performance, complexity, and cost of securing them are often too high.
This is the gap that Bomfather and NeuralRack AI are solving together!
We are trying to solve a simple problem with significant implications. How do you give users access to extremely powerful, affordable GPUs without security issues?
Read more about this collaboration in our blog post!
Our recent blog posts were featured in the Cilium/eBPF community newsletter eCHO News 94. Big thanks to the community for the shoutout!
See the newsletter mention: eCHO News 94 on LinkedIn.
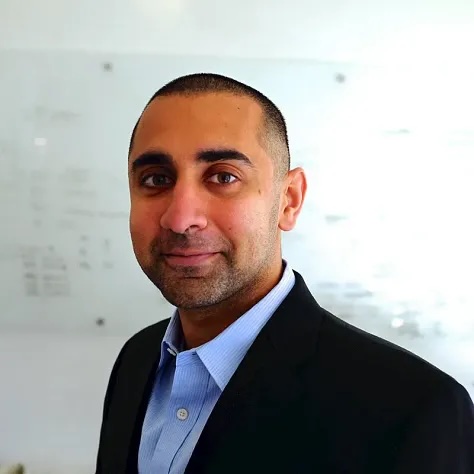
We’re excited to announce that Bomfather has secured funding from Balaji Srinivasan, former CTO of Coinbase and one of the most respected voices in technology.
This investment validates our mission to revolutionize AI security through kernel level protection and will accelerate our development of revolutionary security.
The investment comes at a crucial time as organizations worldwide grapple with the security implications of AI deployment. Bomfather’s unique approach allows for protection with ultra easy integration and a minimal performance overhead.
Thank you for trusting us, Balaji!
We’re excited to announce the publication of our research paper “Bomfather: An eBPF-based Kernel-level Monitoring Framework for Accurate Identification of Unknown, Unused, and Dynamically Loaded Dependencies in Modern Software Supply Chains” on arXiv.
The paper introduces our revolutionary approach to software supply chain security, which addresses critical gaps in conventional dependency-tracking methods.
Our research demonstrates how kernel-level monitoring can provide tamper evident build time dependencies by computing cryptographic hashes of files accessed during compilation and constructing Merkle trees based on observed file content.
Unlike traditional static analysis approaches, our methodology accounts for:
This results in significantly more precise Software Bills of Materials (SBOMs) and enhances trustworthiness in software artifacts through kernel-level evidence of build provenance.